Microsoft estimates Edge Lockdown Mode could have blocked about 60% of real-world privilege escalation attacks, at the cost of a few sites running poorly.
- Edge Canary is testing Lockdown Mode, which disables WebGL, WebGL2, and WebGPU
- Aimed at journalists, executives, security researchers, and administrators
- Microsoft estimates it would have blocked about 60% of real-world privilege escalation attacks targeting Edge
- Games and map sites may break, with per-site exceptions planned
- How to enable: Canary channel, #edge-sdsm-plus flag, Strict mode
Table of Contents
Edge adds a hardened mode for users who are being targeted
Microsoft is developing a new security feature for Edge called Lockdown Mode, borrowing both the idea and the name from Apple's mode of the same name. It works by switching off three graphics APIs entirely, WebGL, WebGL2, and WebGPU, to shrink the surface attackers can exploit. The mode builds on Edge's Enhanced Security Mode (internally known as Super Duper Secure Mode), which already disables Just-In-Time (JIT) compilation in the V8 pipeline, so it can be seen as an extra layer of hardening on top of the old one.
Lockdown Mode is optional, meant for people who accept lower site compatibility in exchange for tighter defenses. According to Gareth Evans, a manager on Microsoft's Partner Security Group, the mode targets people at risk of targeted attacks, such as journalists, executives, security researchers, and administrators, as well as devices running in tightly restricted environments. The trade-off is that sites relying on the disabled APIs, especially those with interactive graphics like games or maps, may not work as usual when you turn this feature on.
Why Microsoft is targeting the GPU process
The first round of testing focuses on the GPU process, a component with higher privileges than usual that has to handle complex graphics tasks passing through browser code, third-party libraries, and device drivers. With WebGL, WebGL2, and WebGPU blocked, a web page can no longer use them to carry out privilege escalation or sandbox escapes. Microsoft estimates that, had the feature existed earlier, it would have blocked about 60% of real-world privilege escalation attacks against Edge users.
Microsoft says it will expand the feature in upcoming releases. The results of this test will shape the final form of Lockdown Mode, including a clearer description of the restricted capabilities and a per-site exception mechanism, so trusted sites keep working normally without weakening protection elsewhere.
How to try it on Edge Canary
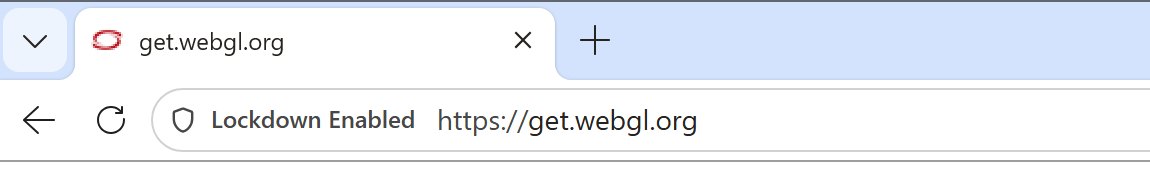
To try it, switch to the Edge Canary channel, enable the #edge-sdsm-plus flag, and restart the browser. Then go to "Enhance your security on the web," choose Strict mode, and turn on blocking for WebGL graphics and WebGPU graphics. When the feature is active, the address bar shows a "Lockdown Enabled" label each time a page is blocked from using WebGL or WebGPU, so you can tell why a graphics-heavy page isn't behaving as expected.
Edge has been tightened in other areas as well. Last year, Microsoft added a scareware sensor so Defender SmartScreen can block scam pages faster, and it restricted access to Edge's Internet Explorer mode after hackers were found using a zero-day flaw in the Chakra JavaScript engine to break into target devices.
The approach makes sense because the GPU process is a complex, highly privileged component, so cutting off the paths into it is a fairly direct way to reduce risk. However, the 60% figure is Microsoft's own estimate, so treat it as a positive sign rather than an independently verified conclusion. For ordinary users in Vietnam, the feature isn't necessary, since games, maps, and web graphics would run noticeably worse. If you work in journalism, system administration, or security research, it's worth trying on Canary, and it's best to wait until per-site exceptions are finished before considering it for daily use.
Source: BleepingComputer
Reviewed by: Hero Association